
JWT Decoder & Claims Inspector
Secure, client-side JSON Web Token parser. Inspect headers, payload claims, and sign HMAC signatures instantly in full privacy.
Inspection Workspace
Paste an encoded JWT on the left to inspect its parameters, decode payloads, and verify signatures instantly.
What is a JSON Web Token?
JSON Web Tokens (JWT) are an open standard (RFC 7519) that defines a compact, URL-safe way to securely transmit structured data between client and server as a JSON object.
Encoding vs. Cryptographic Verification
Encoding formats JSON payload claims into a URL-safe Base64url string. Cryptographic Verification, however, validates that the token was signed with a HMAC secret or public key and has not been tampered with.
Who Uses JWTs and Why?
Modern engineering teams use JWTs for stateless authentication (Single-Sign-On), API authorization, and secure information exchange. They operate completely offline on the client side with no database lookup overhead.
JWT, Base64, and URL Encoding Explained
Demystify data encoding formats. Learn how JSON Web Tokens work, when to use Base64, URL encoding, Hex, Binary, and Unicode standards to transmit and structure backend data safely.
Read the Complete Guide➔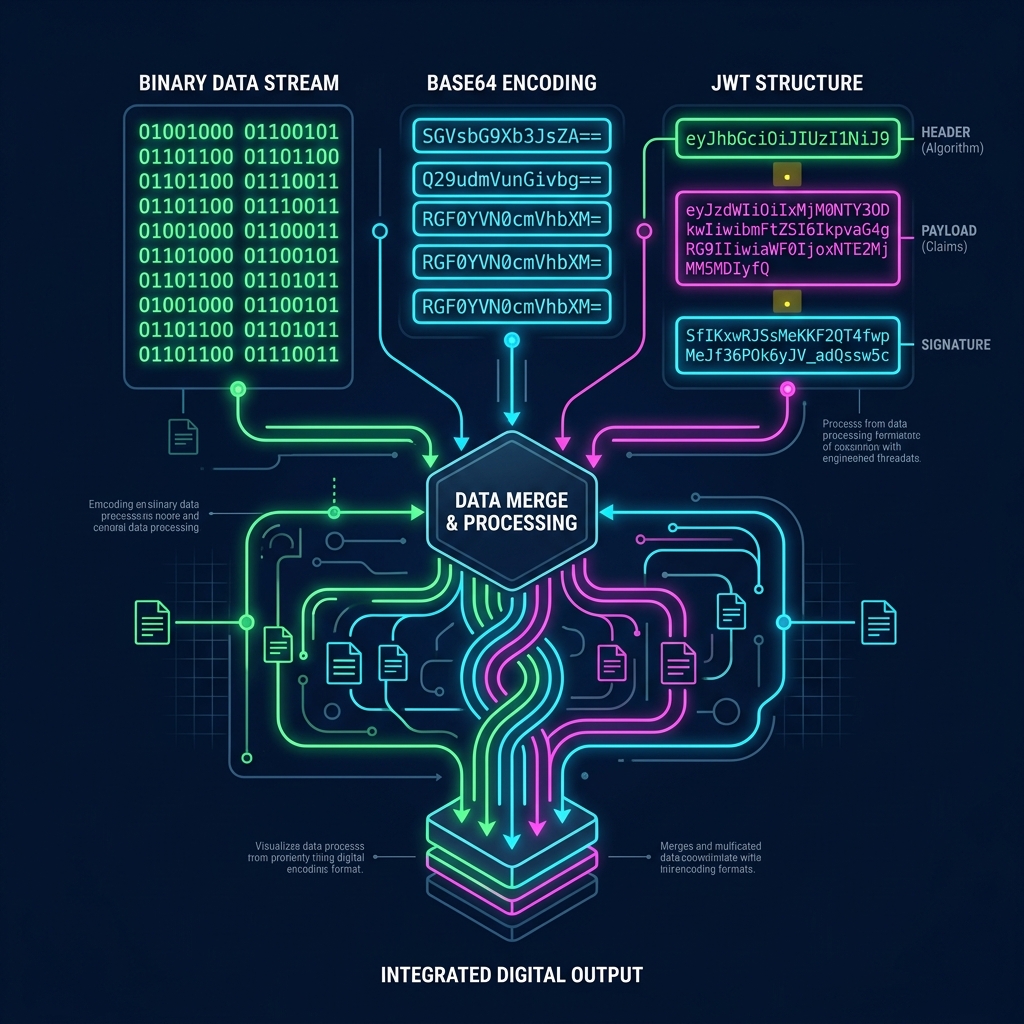
Overview & Capabilities
Decode, inspect, and analyze JSON Web Tokens (JWT) with our client-side JWT Decoder! Paste any JWT string to instantly parse its Header, Payload claims, expiration timestamps (exp, iat, nbf), signature algorithm (RS256, HS256, ES256), and human-readable time-to-expiry indicators with 100% offline privacy.
How to Use
header.payload.signature format) into the input box.Key Features
exp, iat) into local dates and relative countdown timers.iss (Issuer), sub (Subject), aud (Audience), and exp.Common Use Cases
Tips & Best Practices
alg header to ensure it matches your expected algorithm (e.g., RS256).exp claim is in seconds (Unix time). Our tool converts this for you automatically.Related Tools

Base64 Encoder & Decoder Online
Encode and decode Base64 strings, UTF-8 text, and binary files online. Supports standard RFC 4648, URL-Safe Base64URL, and image Data URIs. 100% Free.

Hash Generator Online
Generate and verify cryptographic hashes online: SHA-256, SHA-512, MD5, SHA-1, SHA3, and Keccak-256 for text and files. 100% Client-Side Privacy. Free.

Certificate Decoder Online
Decode and inspect X.509 SSL/TLS certificates (PEM / CRT / CER) online. View Subject, Issuer, Validity dates, SANs, Public Key, and fingerprints. 100% Private.

URL Encoder & Decoder Online
Encode and decode URLs, URI components, and query parameters online. Features RFC 3986 percent-encoding and UTF-8 special character handling. 100% Free.

Interactive JSON Studio
Professional online JSON editor to format, validate, minify, diff, and query JSONPath. Convert CSV, XML, and YAML to JSON. Generate TypeScript & Zod types. Free.
Frequently Asked Questions
Q Is it safe to paste production JWT tokens containing credentials into this decoder?
Yes, 100%. All decoding operations run locally in your browser's JavaScript sandbox. No tokens, secret claims, or authorization credentials are ever sent to external servers.
Q What are the three parts of a JSON Web Token?
A JWT consists of three Base64URL-encoded parts separated by dots: 1. Header (algorithm and token type), 2. Payload (claims and user data), 3. Signature (cryptographic hash validating token authenticity).
Q How does the decoder check if a JWT has expired?
The decoder reads the numeric `exp` (expiration) timestamp from the payload, converts it from Unix epoch seconds to milliseconds, and compares it against `Date.now()`.